Oct 15, 2026 by Anthony York (YorkSoft Ltd)
Last Updated: 14 October 2026
A national survey of 1,000 small and medium business leaders found a clear gap between how confident they feel about cyber security and how ready they actually are, according to the 2026 Small Business Cybersecurity Awareness & Practices Survey. Digital security best practices for small businesses are the practical steps that close that gap: controlling who gets in, spotting fake messages, and keeping recoverable copies of your data.
At YorkSoft Ltd, we build and maintain web applications for firms, so we see where small teams are most exposed. Below, we break down the steps that matter most, in the order we would tackle them.
Most breaches aimed at small firms are not sophisticated. They are a lost password, a clicked link, or a backup that was never tested. That is good news: the fixes are cheap and repeatable.
Multi-factor authentication (MFA) is a login method that asks for a second proof of identity, such as a code from your phone, alongside your password. It is the single highest-value change most small firms can make this week.
The UK government's guidance for small businesses lists enforcing MFA, requiring it for every administrator account, patching systems, and testing backups as core actions. Start with the accounts that can do the most damage.
Your email, finance, and website admin logins are the keys to everything else. If an attacker takes one, they can reset the rest.
The Information Commissioner's Office (ICO) recommends restricting sensitive information to the people who need it for their jobs. In practice, that means a marketing assistant should not be able to see payroll.
Phishing prevention for small businesses starts with teaching staff what a fake message looks like, then backing that training with technical controls that catch what people miss.
Phishing is a message that pretends to be from someone you trust to get you to click a link, open a file, or send money. Small teams are targeted because they often lack the filtering and reporting habits of larger firms.
The payment rule matters most. Invoice fraud, where a supplier's email is spoofed to redirect a payment, costs firms real money and rarely needs any technical skill.
Small business data backup best practices follow one rule: keep three copies of your data, on two types of storage, with one held off-site. This is the 3-2-1 rule, and it is the difference between a bad day and a closed business.
Backups only count if you can restore from them. A copy you have never opened is a hope, not a plan.
Ransomware spreads to anything it can reach, including a backup drive that stays plugged in. An offline or immutable copy is the one attackers cannot encrypt.
| Backup Layer | What It Covers | How Often | Who Checks It |
|---|---|---|---|
| Cloud backup | Files, email, site data | Daily, automatic | Office manager |
| Local drive | Fast restore of key files | Weekly | IT lead |
| Off-site copy | Fire, flood, theft | Monthly | Director |
A small business cyber security policy template is a short written document that sets out who does what, so security does not depend on one person remembering. Keep it to two pages.
Write it in plain language and name a person for each task. A policy nobody can follow is worse than none, because it creates false confidence.
Give every new starter the policy on day one and ask them to confirm they have read it. That single step turns a document into a habit.
A small business cyber security checklist turns the advice above into a set of tasks you can tick off in order. Work top to bottom, and do not skip the admin accounts.
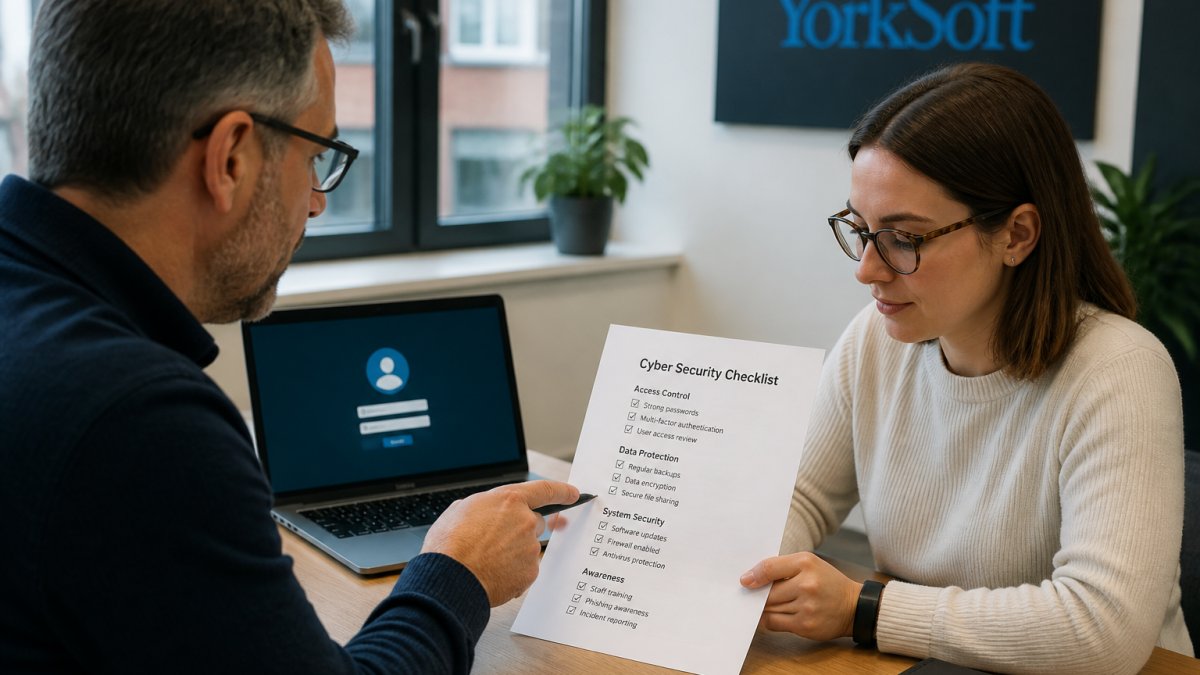
If your website or web app handles customer logins, the same list applies to it. Our team builds access control and monitoring into our web development work as standard, so the technical side does not rest on memory.
Most small firms do not need a large security budget. They need the basics done properly, checked often, and owned by someone.
If you would rather not carry that alone, YorkSoft Ltd can help. We offer rank monitoring, keyword research and analysis, backlink analysis, competitor monitoring, and high-quality link building, alongside web development and custom web applications. If your site or app needs secure access control, tested backups, or a technical review, get in touch with our team and we will look at your setup with you.
Get started with YorkSoft Ltd and put your digital security on a firm footing.
Start with four measures that cover most real-world risk: enforce multi-factor authentication on every account, especially administrator logins; restrict access to sensitive data by job role; patch systems and devices promptly; and keep tested, offline backups. Add phishing awareness training and a written policy so staff know what to do. The 2026 Small Business Cybersecurity Awareness and Practices Survey found a gap between how confident SME leaders feel and how ready they actually are, so treat this as a checklist to verify, not assume.
Phishing remains the most common way attackers get in. Train staff to check the sender's full address, treat urgent payment or password requests as suspicious, and verify unusual instructions by phone using a number they already hold. Turn on MFA so a stolen password alone is not enough, and configure email filtering to flag external senders. Run short, regular test exercises rather than a one-off session, and make reporting a suspicious email quick and blame-free so people actually do it.
Daily for anything you could not recreate, with backups stored in at least three places: the live system, a local device, and an offsite or cloud copy. Follow the 3-2-1 approach and, critically, test a restore every quarter. An untested backup is an assumption, not a safeguard. The UK government's guidance for small organisations lists performing and testing backups alongside patching and MFA as core recommended actions, and ransomware attacks specifically target connected backups, so keep at least one copy offline or immutable.
Yes, even a short one. A written policy sets out who is responsible for what, how access is granted and removed when staff leave, how incidents are reported, and what devices and software are permitted. It also gives you something concrete to review annually and to hand to insurers or clients who ask about your controls. A two-page document covering passwords, MFA, backups, device use and incident reporting is far more useful than a lengthy template nobody reads.